Map your surface
We continuously map every subdomain, endpoint, server, and application. The complete digital footprint, including the bits you forgot.
Every engagement is delivered through the DERISK PTaaS Platform, enabling real-time collaboration, live reporting, on-demand retesting, remediation tracking, asset management, executive dashboards, and native Jira & Slack integrations — transforming penetration testing into a continuous security workflow rather than a one-time assessment.
DERISK is built for organisations operating in the UAE and the wider GCC region. Every finding is tagged to the specific regional regulation it violates, so your compliance team gets evidence-ready mappings without reinterpretation.
Every finding is tagged to the control it violates, so your compliance team gets evidence-ready mappings instead of a pile of raw vulnerabilities to interpret.
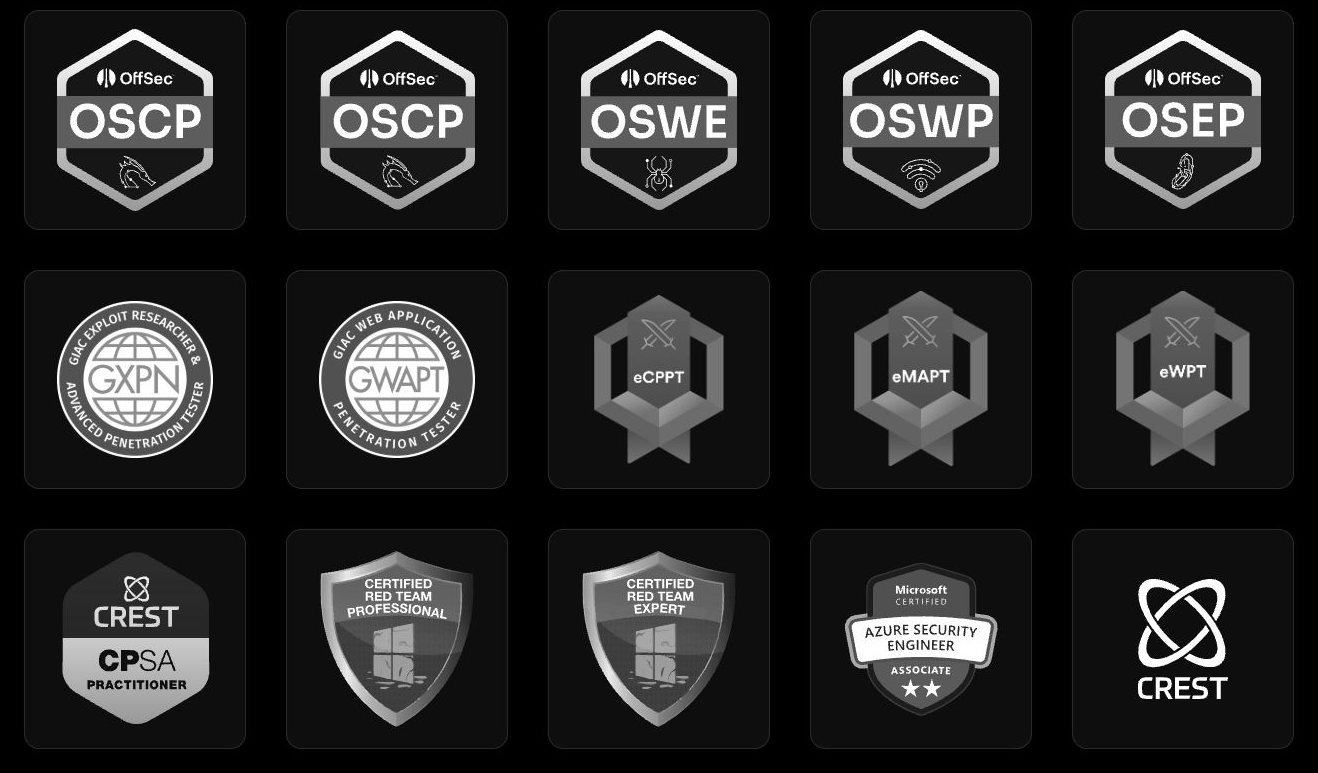
Our testers hold industry-recognised certifications across offensive security, cloud, red teaming, and specialised domains — so your testing is always led by proven practitioners, not junior analysts running scanners.
No vague “days” or “weeks.” These are the concrete delivery commitments baked into every DERISK engagement.
Initial confirmed vulnerabilities appear on your portal within 8 hours of engagement kickoff — not after a weeks-long report cycle.
Critical and high-severity findings are validated, PoC-documented, and published within 2 hours of discovery.
Remediation retests are completed within 24 hours of you marking a finding as fixed — no separate engagement or extra cost.
A complete engagement report with executive summary, technical detail, and compliance mapping is delivered within 2 business days of engagement close.
Attackers move quickly. The teams that stay ahead measure exposure continuously and close the paths that matter most.
Continuous penetration testing gives your team the visibility to find, fix, and verify before a weakness becomes an incident.
DERISK combines agentic AI with certified offensive-security experts to run a continuous five-stage pipeline — mapping, hunting, proving, validating, and retesting. No dashboards to babysit, no noise — just proven attack paths and expert-validated risk, delivered transparently.
Traditional pentesting gives you a snapshot in time. DERISK gives you always-on assurance: your attack surface is monitored continuously, weaknesses are hunted at machine speed, and every finding is confirmed by a human before it reaches you.
We continuously map every subdomain, endpoint, server, and application. The complete digital footprint, including the bits you forgot.
Agentic AI probes your footprint continuously, thinking like an attacker to uncover misconfigurations, exposures, and exploitable paths at machine speed.
Every finding is safely exploited and chained to confirm real impact, so you see proven attack paths, not theoretical vulnerabilities.
Our offensive security specialists review and confirm each result, cutting the false positives and leaving only risk that’s real and actionable.
Fixes are verified on demand and your surface is continuously monitored, turning point-in-time testing into always-on assurance.
Why teams choose Penetration Testing as a Service over traditional engagements.
Penetration Testing as a Service (PTaaS) is a modern, continuous approach to security testing that replaces one-off engagements with an ongoing partnership. Expert penetration testers simulate real-world attacks across your applications, infrastructure, APIs, and cloud environments, while a collaborative platform delivers real-time findings, streamlined remediation, and rapid retesting. Augmented by agentic AI that tests autonomously between human-led assessments, PTaaS gives your organisation continuous visibility into your security posture — so testing keeps pace with the speed of your business, not the pace of a quarterly report.
Launch penetration tests from the platform whenever you need them. Start, audit, and stop engagements in real time — no more waiting for the next scheduled compliance cycle.
Findings live on the platform instead of buried in PDF reports. Results are searchable, always up to date, and instantly available to your entire security team and downstream systems.
Automated re-testing confirms fixes hold and surfaces new exposures as your environment changes, so your risk posture improves every week instead of once a year.
Comprehensive vulnerability assessment and penetration testing across your entire digital footprint.
DERISK evaluates web applications to identify vulnerabilities that could allow attackers to compromise sensitive information, bypass security controls, or gain unauthorised access. Our assessments cover application functionality, authentication and authorisation mechanisms, session management, input validation, business logic, and common web application vulnerabilities aligned with industry standards such as OWASP Top 10.
Web App Pentest details ↗DERISK assesses the security of Android and iOS applications by simulating real-world attacks against mobile platforms. Our testing identifies weaknesses related to application security controls, data storage, authentication mechanisms, communication channels, reverse engineering risks, and insecure configurations that may impact user data or application integrity.
Mobile App Pentest details ↗DERISK performs comprehensive API security assessments to identify vulnerabilities that could expose sensitive data or enable unauthorised access to backend services. Testing includes authentication and authorisation controls, access management, input validation, business logic testing, API endpoint analysis, and security configuration reviews.
API Pentest details ↗DERISK’s Network Penetration Testing service provides end-to-end assessment of your network infrastructure by simulating real-world attacks across four key areas: External Network Penetration Testing, Internal Network Penetration Testing, Active Directory Penetration Testing, and Wi-Fi Penetration Testing. Our assessments identify weaknesses that could enable unauthorised access, privilege escalation, lateral movement, or compromise of critical systems across your entire network estate.
Network Pentest details ↗DERISK provides visibility into an organisation’s external attack surface by identifying exposed assets, internet-facing systems, domains, services, and potential entry points. The assessment helps organisations discover unknown risks, identify security gaps, and understand their exposure from an attacker’s perspective.
Attack Surface Pentest details ↗DERISK assesses cloud environments to identify security risks across cloud infrastructure, identity and access management, configurations, and deployed services. Our testing helps organisations detect misconfigurations, excessive permissions, insecure deployments, and other cloud security weaknesses.
Cloud Security Assessment details ↗DERISK performs manual and automated source code reviews to identify security vulnerabilities and insecure coding practices early in the software development lifecycle. Our experts analyse application code to detect issues such as hardcoded credentials, insecure functions, authentication weaknesses, improper input handling, and vulnerabilities that may introduce security risks.
Source Code Review details ↗DERISK runs Dynamic Application Security Testing to automatically detect vulnerabilities in running web applications from the outside in. By interacting with the live application in real time, DAST uncovers issues such as injection flaws, broken authentication, misconfigurations, and exposed sensitive data — complementing manual testing with continuous automated coverage between full assessments.
DAST details ↗DERISK performs systematic vulnerability scanning across infrastructure, applications, and cloud assets to identify known security weaknesses and misconfigurations. The assessment provides a prioritised view of your exposure, enabling teams to address the most urgent risks first while feeding results directly into the DERISK platform for tracking and remediation.
Vulnerability Assessment details ↗Beyond VAPT, we offer a full spectrum of security services to support your organisation before, during, and after an incident.
DERISK’s Incident Response service provides rapid, expert-led support to help organisations detect, contain, eradicate, and recover from cybersecurity incidents. Our team works alongside your organisation to minimise impact, preserve evidence, and restore normal operations as quickly as possible while providing clear communication throughout the engagement.
Incident Response details ↗DERISK’s Digital Forensics service provides meticulous investigation and analysis of digital evidence to support incident response, legal proceedings, internal investigations, and regulatory compliance. Our forensic experts use court-admissible methodologies to preserve, collect, examine, and report on digital evidence from systems, mobile devices, and cloud environments.
Digital Forensics details ↗DERISK’s Security Assessment service provides a comprehensive evaluation of your organisation’s overall security posture across people, processes, and technology. We assess your security controls, policies, architecture, and risk management practices against industry standards to identify gaps and provide a prioritised roadmap for improvement.
Security Assessment details ↗DERISK’s Security Configuration Review service evaluates the configuration of your systems, applications, and network devices against industry-recognised hardening standards. We identify misconfigurations, insecure defaults, and deviations from best practices that could expose your organisation to attack, providing clear remediation guidance to harden your environment.
Configuration Review details ↗DERISK’s Malware Analysis service provides in-depth reverse engineering and behavioural analysis of malicious software to understand its capabilities, persistence mechanisms, and impact on your environment. Our analysts use static and dynamic techniques to dissect malware samples and deliver actionable intelligence for incident response and threat hunting.
Malware Analysis details ↗Why organisations are moving from traditional engagements to continuous testing.
PTaaS replaces the annual penetration test with a continuous engagement. Expert testers simulate real-world attacks across your applications, infrastructure, APIs and cloud, while a platform delivers findings in real time rather than in a PDF weeks later. Agentic AI tests autonomously between human-led assessments, so coverage keeps pace with how often you ship.
Initial confirmed findings appear within 8 hours of kickoff, critical and high-severity issues are validated and published within 2 hours of discovery, remediation retests complete within 24 hours, and the full report is delivered within 2 business days of engagement close.
Every finding is tagged to the specific control it violates across ISO 27001, SOC 2, PCI DSS, HIPAA and GDPR, plus the UAE and GCC regional regimes — DESC ISR, UAE Information Assurance, NESA and Central Bank of the UAE requirements. Your compliance team gets evidence-ready mappings rather than raw vulnerabilities to reinterpret.
Yes. DERISK is headquartered in Dubai Silicon Oasis and delivers across the GCC — Saudi Arabia, Qatar, Kuwait, Bahrain and Oman — with findings mapped to each market’s regulator, including NCA ECC and SAMA CSF in Saudi Arabia.
No. Agentic AI provides scale and continuity: it maps your attack surface, probes it around the clock and chains techniques faster than a human could. Judgement stays human — every finding is reviewed and confirmed by a certified offensive security specialist before it reaches you, which is how we deliver zero false positives.
Book a demo and see how DERISK delivers real-time findings, expert-validated vulnerabilities, and continuous retesting — all in one platform.